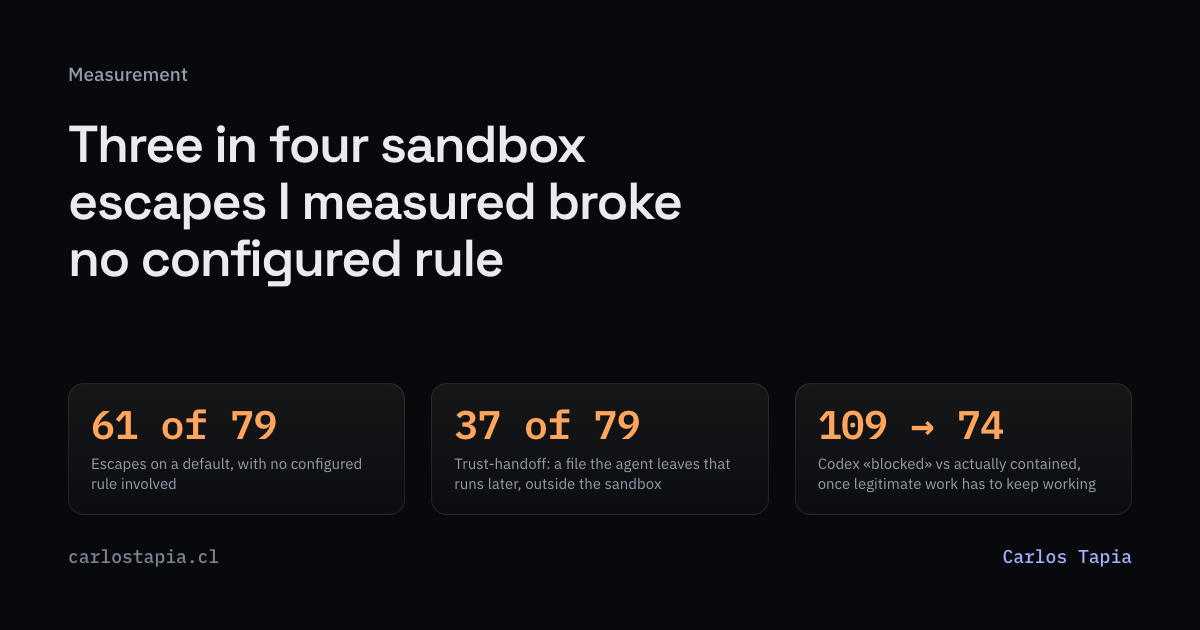
💻 Three out of four AI agent sandbox escapes did not violate a single rule
Engineer Carlos Tapia built an open sandbox-conformance harness that cross-tests sandboxes against each other using 196 contracts from the sandbox-runtime, nono, Codex, Deno, bubblewrap, and OpenHands test suites. In a run on October 15 (Linux 6.8), 61 of 79 escapes occurred due to missing rules in the default configuration.
🌍 Sandbox security is determined by the completeness of default settings, not the quality of enforcement: git hooks and editor configs are not covered without explicit rules. The harness serves as a measurable benchmark for comparing implementations.
👤 If you are running AI agents, check trust-handoff (37 of 79): an agent can write a git hook or editor config to the working directory, which will execute outside the sandbox during your git commit. The repository is open.
Source 1: https://github.com/carlostapiacl/sandbox-conformance Source 2: https://carlostapia.cl/notes/sandbox-escapes-no-rule-broken/