
Engineer Joseph Spurrier, with the help of the Claude model (Opus 4.6), brought back to life the Hello Sense sleep tracker, which stopped working after the company shut down and its cloud infrastructure was disabled. Relying on source code published by the vendor, he built a local replacement for the server backend and uploaded the restored stack to GitHub under the MIT license. The case is notable for the distribution of roles: the model quickly generated auxiliary scripts, but the decisive hardware problem was solved by a human.
What happened
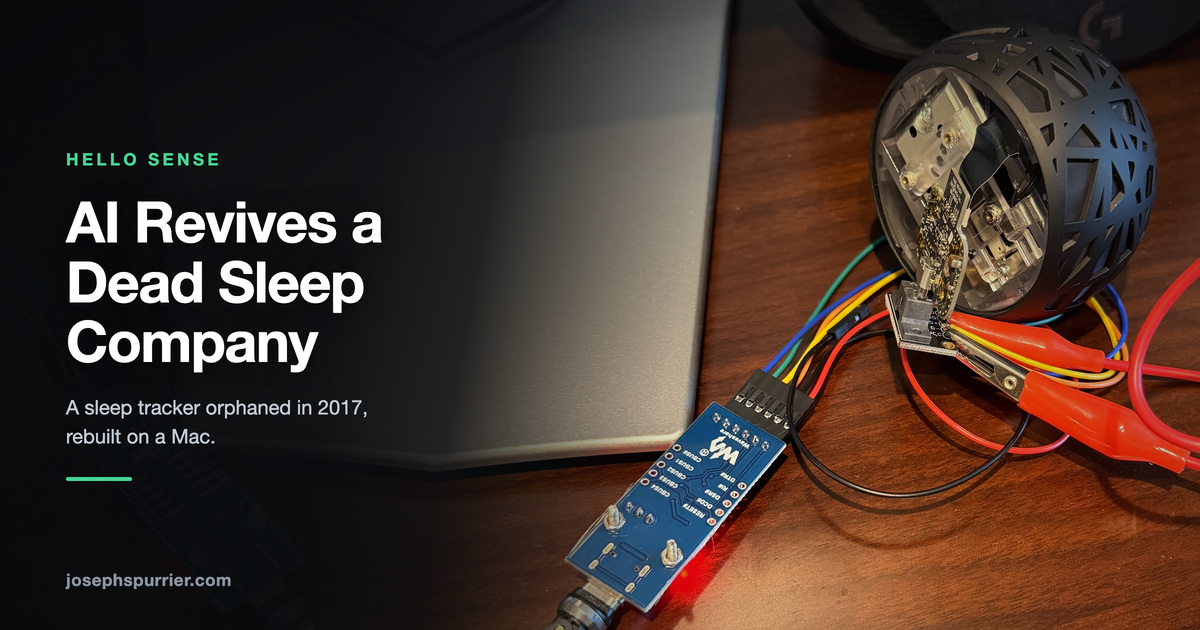
Joseph Spurrier took the dead Hello Sense — a "glowing sphere" with temperature, humidity, light, noise, and air quality sensors — and managed to restart the device without the Hello company's servers, which were shut down on June 3, 2017. On GitHub, he found almost all of the vendor's code: the kitsune firmware for the TI CC3200 hub and kodobannin for the Sleep Pill on the Nordic nRF51422, five Java services suripu, and the iOS app suripu-ios. The obstacles were the unique 128-bit AES key of each instance and the method of entering the CC3200 bootloader, which had not been disclosed to the community. The key breakthrough occurred on July 26, 2026: the micro connector ID pin, which in the CC3200 performs the role of SOP2, the bootloader selection input, needs to be connected not to 5 V, but to the RTS line of the FTDI adapter, because the 5-volt logic of the TXD, RXD, and RTS lines interfered with the transfer of control. Further work proceeded in conjunction with the model: Claude generated six probe scripts for UART in 24 minutes, although the author himself, as he frankly admits, did not think of the 3.3-volt wiring. The final step was the replacement of the cloud infrastructure: instead of the 16 containers of the original Hello cloud, a stack of three components was launched, the Go service orb, orb-algo with Hello's untouched Java algorithms, and Postgres with LocalStack instead of AWS, and the connection of the device to the local server was provided by intercepting DNS requests to the hello.is domain, its own certificate authority, and the pure Python library tlslite-ng for the TLS handshake of a decade ago.
Context
Hello Sense grew out of the startup Hello, which attracted about $40 million in investment, including a round from Temasek in 2015, and another $2.4 million on Kickstarter. The business did not survive the market: after the company closed, the cloud servers were shut down, and the working hardware lost some of its functions, because the logic worked not only in the device but also on the cloud side. For the Internet of Things, this is a typical fate: a gadget tied to someone else's infrastructure ends with it, even if it is completely in working order. The rarity of the case is that Hello managed to publish most of the code in the public domain, and it was this decision that in hindsight turned out to be a life preserver, allowing an enthusiast to recreate the missing parts independently. Around such projects, a practice of "digital archaeology" has developed: searching for source code, extracting keys, replacing certificates, and building one's own backend for abandoned brand equipment. The hello-sense task fits into the growing movement for devices to continue working after the death of the vendor, if its code is available to the community.
Why this is important for the industry
The industry reads two lessons from the case. The first is methodological: an agentic LLM takes on the routine of investigating an unknown system, from writing probe scripts to analyzing outdated protocols, so reviving abandoned equipment no longer requires years of expertise in all the stacks involved. At the same time, the author of the report honestly records the limit of this usefulness: the hardware breakthrough with the voltage wiring was made by a human, meaning the working scheme is the complementarity of domain knowledge and generation speed, not the autonomy of the model. This pattern is important for teams integrating agents into engineering processes. The second lesson is product: a device dependent on the vendor's cloud lives exactly as long as its servers, and the only insurance for buyers turned out to be the source code published in advance. For vendors, this is an argument to open the code when closing a line, for device owners — a signal to take into account the risk of "cloud death" when choosing gadgets. Expectedly, within a six-month horizon, repetitions of the recipe on other orphaned devices and the first generalized utilities for UART and SWD archaeology with LLM participation will appear, and within a two-year horizon, local backends for the hardware of dead vendors may form into a sustainable practice; the response of manufacturers will probably be the strengthening of hardware protection like secure element.
Why this is important for users
For a reader with a gadget abandoned by the manufacturer, the case provides a step-by-step route, not a one-time hack. The josephspurrier/hello-sense repository on GitHub is released under the MIT license, the guides SENSE_SETUP.md and PILL_RECOVERY.md describe the path line by line, including the rescue of the "bricked" Sleep Pill via SWD through the J-Link debugger, the hub firmware build 4513 was rebuilt byte by byte from the source code, and the iOS app was restored in Swift 3, so repeating the path does not require reverse engineering from scratch. The generalized sequence for similar equipment is as follows: find the vendor's open repositories, extract the unique device key via UART or SWD, replace the TLS certificates, and launch your own local backend in Docker. An important framework: the route works only when the manufacturer left the code, and the keys are technically readable; the scenario with a completely closed firmware is not covered by this recipe.
What is still unknown / limitations
The main caveat is the scale of the sample: the case is a single one, with a pronounced survivor bias, because the path worked because the vendor had published the source code in advance, the device key was in the flash at the path /cert/key.aes, and the broken clocks were off by only decades, which allowed them to be bypassed with a certificate dated 1950. The contribution of the model is not measured: there is no comparison of time and number of iterations with and without Claude in the material, and the original source's headline "AI Revives a Dead Sleep Company" attributes more to the model than the author himself admits. There is no independent verification either: the discussion on Hacker News was limited to 2 points and 0 comments, so we are faced with a well-documented field report, not the result of a controlled measurement. The assessment of the case as the "first sufficiently complete reproducible playbook" looks like an excessive generalization, and the forecasts about the replication of the methodology and ready-made sets for revival require verification by time.
Sources
- Joseph Spurrier — AI Revives a Dead Sleep Company
- GitHub — josephspurrier/hello-sense: Self-Hosting the Defunct Hello Sense
- Hacker News — AI Revives a Dead Sleep Company (discussion)
Author
Look at AI, editorial team